This signifies that TLM provides more natural modeling of protocols on the basis of their buildings than the tactic of Zahednejad et al. Our proposed model performs finest on both randomly generated protocols and sensible protocols. These results show that our model has a better inductive bias for coping with cryptographic protocols. To design complex and correct cryptographic protocols, designers usually use computer aids such as automated verification instruments. As we input the protocol specification and safety requirements, a super automated verification device immediately outputs whether or not the protocol satisfies the safety necessities or not. A typical example of such an computerized verification software is a proper verification software primarily based on model checking.
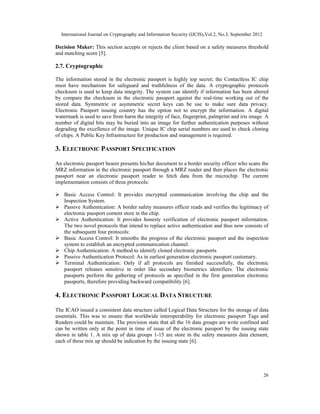
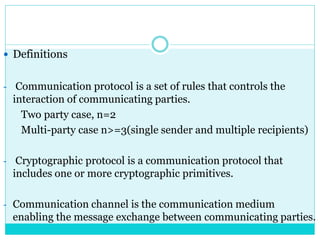
Cryptographic Protocols And Strategies
Protocols should allow change, implementations should help it, organizations must plan for it, and architectures should accommodate real-world constraints. Sustaining crypto agility subsequently requires ongoing coordination across protocol design, implementation practices, governance technique, and hardware constraints, with continuous reassessment as risk models, requirements, and computational capabilities evolve. NIST describes this method utilizing ideas corresponding to cryptographic gateways or “bump-in-the-wire” solutions, which intercept information flowing into and out of a legacy system.
The most elementary model taking a fixed-length vector as an input is named multi-layer perceptron (MLP). Vectors computed in the deep studying mannequin are referred to as latent vectors of the enter knowledge and thought of to characterize advanced options of the information. Relying on the construction and prior information of the enter information, an appropriate model structure ought to be chosen.
Digital Signature Algorithm (dsa)
This is often achieved through encryption — lined in § 7.2 Asymmetric encryption and § 7.1 Symmetric encryption — which converts readable information (plaintext) into ciphertext that may only be decrypted by licensed events with the right cryptographic key; a widely used instance is the Advanced Encryption Standard (AES), standardized by the united states By leveraging automated enterprise management instruments, adopting zero-trust-aligned controls where essential, and maintaining a Cryptographic Invoice of Supplies (CBOM), organizations remodel cryptographic change from an emergency response right into a ruled, repeatable process. This strategic readiness ensures that cryptographic policies stay enforceable across both agile and constrained environments, permitting organizations to sustain safety, resilience, and trust as cryptographic requirements inevitably evolve.
Modern distributed systems can use service meshes or sidecar proxies to centralise cryptographic coverage https://www.admeve-toys.com/teledildonics-bridging-the-distance-with-smart-intimacy/ enforcement. This abstracts the crypto logic away from particular person microservices, making it easier to update libraries and rotate keys with minimal disruption. Whereas software program libraries normally run in “user space” and are simpler to replace, protocols like IPsec often run in the OS kernel. Agility in the kernel is more difficult because algorithms are sometimes fixed when the kernel is constructed, although designers can improve this by using loadable kernel modules.
Proposed Technique
- Typically, many of these have particular focus areas and governance models, are industry-driven or academia-driven and operate on specific focus areas and governance models with processes which might be open to most of the people.
- As An Alternative of modifying the legacy system itself, cryptographic protections are applied outdoors the system boundary, permitting organizations to improve security without altering the unique hardware or software.
- Indeed, a digital signature is a cryptographic mechanism that enables a sender to signal a message or document in such a way that the sender can not deny having signed the message, because the receiver can cryptographically prove the association between the message and the sender.
- The third process is the verification of cryptographic protocols using a skilled verifier (Figure 2c).Users (e.g., the protocol designer) will confirm the security of cryptographic protocols utilizing the verifier constructed within the second process.Using machine learning, customers can verify cryptographic protocols in practical time, see Part four.4.
To transfer away from this sample, let us understand the significance of specific governance and visibility. Organizations should perceive where cryptography is used, how it’s implemented, and which methods rely upon it. A cryptographic stock turns into the inspiration for understanding and managing cryptographic belongings, offering a comprehensive view of algorithms, key sizes, protocols, libraries, and hardware components in use.
A machine-learning-based verifier is educated on the dataset constructed within the first process. We prepare the model proposed in Part 4.three on the coaching dataset.The number of dimensions of the latent vector of the LSTM and Tree-LSTM in the mannequin is ready to 128.We use RMSprop with batch dimension 100 to optimize the mannequin with 200 parameter updates.The learning fee is ready to 0.001. The second course of is to assemble the protocol verifier utilizing machine learning (Figure 2b).A machine-learning-based verifier is skilled on the dataset constructed in the first process.We describe the construction of the mannequin in Part 4.three. Our cryptographic standards and pointers help safe world e-commerce, defend U.S. federal info and top-secret information, and are utilized in business applications from tablets and cellphones to ATMs. Hybrid key exchanges combine both ECDH and post-quantum key change to scale back the security dangers concerned with post-quantum key exchanges implementations.
Cryptographic Rigidity In Hardware And Long-lived Techniques
The most recommended PBKDF is Argon2id, described in RFC9106, which is a memory-hard function that gives strong security guarantees towards various types of assaults. Argon2id is designed to be efficient in each software and hardware implementations and is widely used in password hashing and key derivation purposes. Cryptographic agility just isn’t about predicting which algorithms will fail subsequent, however about ensuring that failure does not translate into disaster. By embedding agility across technical, operational, and strategic layers, organizations can treat cryptographic evolution as a managed, continuous course of, preserving trust, safety, and resilience in an setting where change is inevitable. Taken collectively, the NIST CSWP 39 presents cryptographic agility as a layered, end-to-end capability.
Leave A Comment